Security

Endpoint Protection with Wazuh

Would you know if a critical file on a server changed overnight? ResorsIT runs Wazuh to watch your hosts for unauthorized changes, known vulnerabilities and weak configuration, and puts what it finds where your team already looks.

File integrityVulnerability scanningConfiguration assessmentCompliance reports
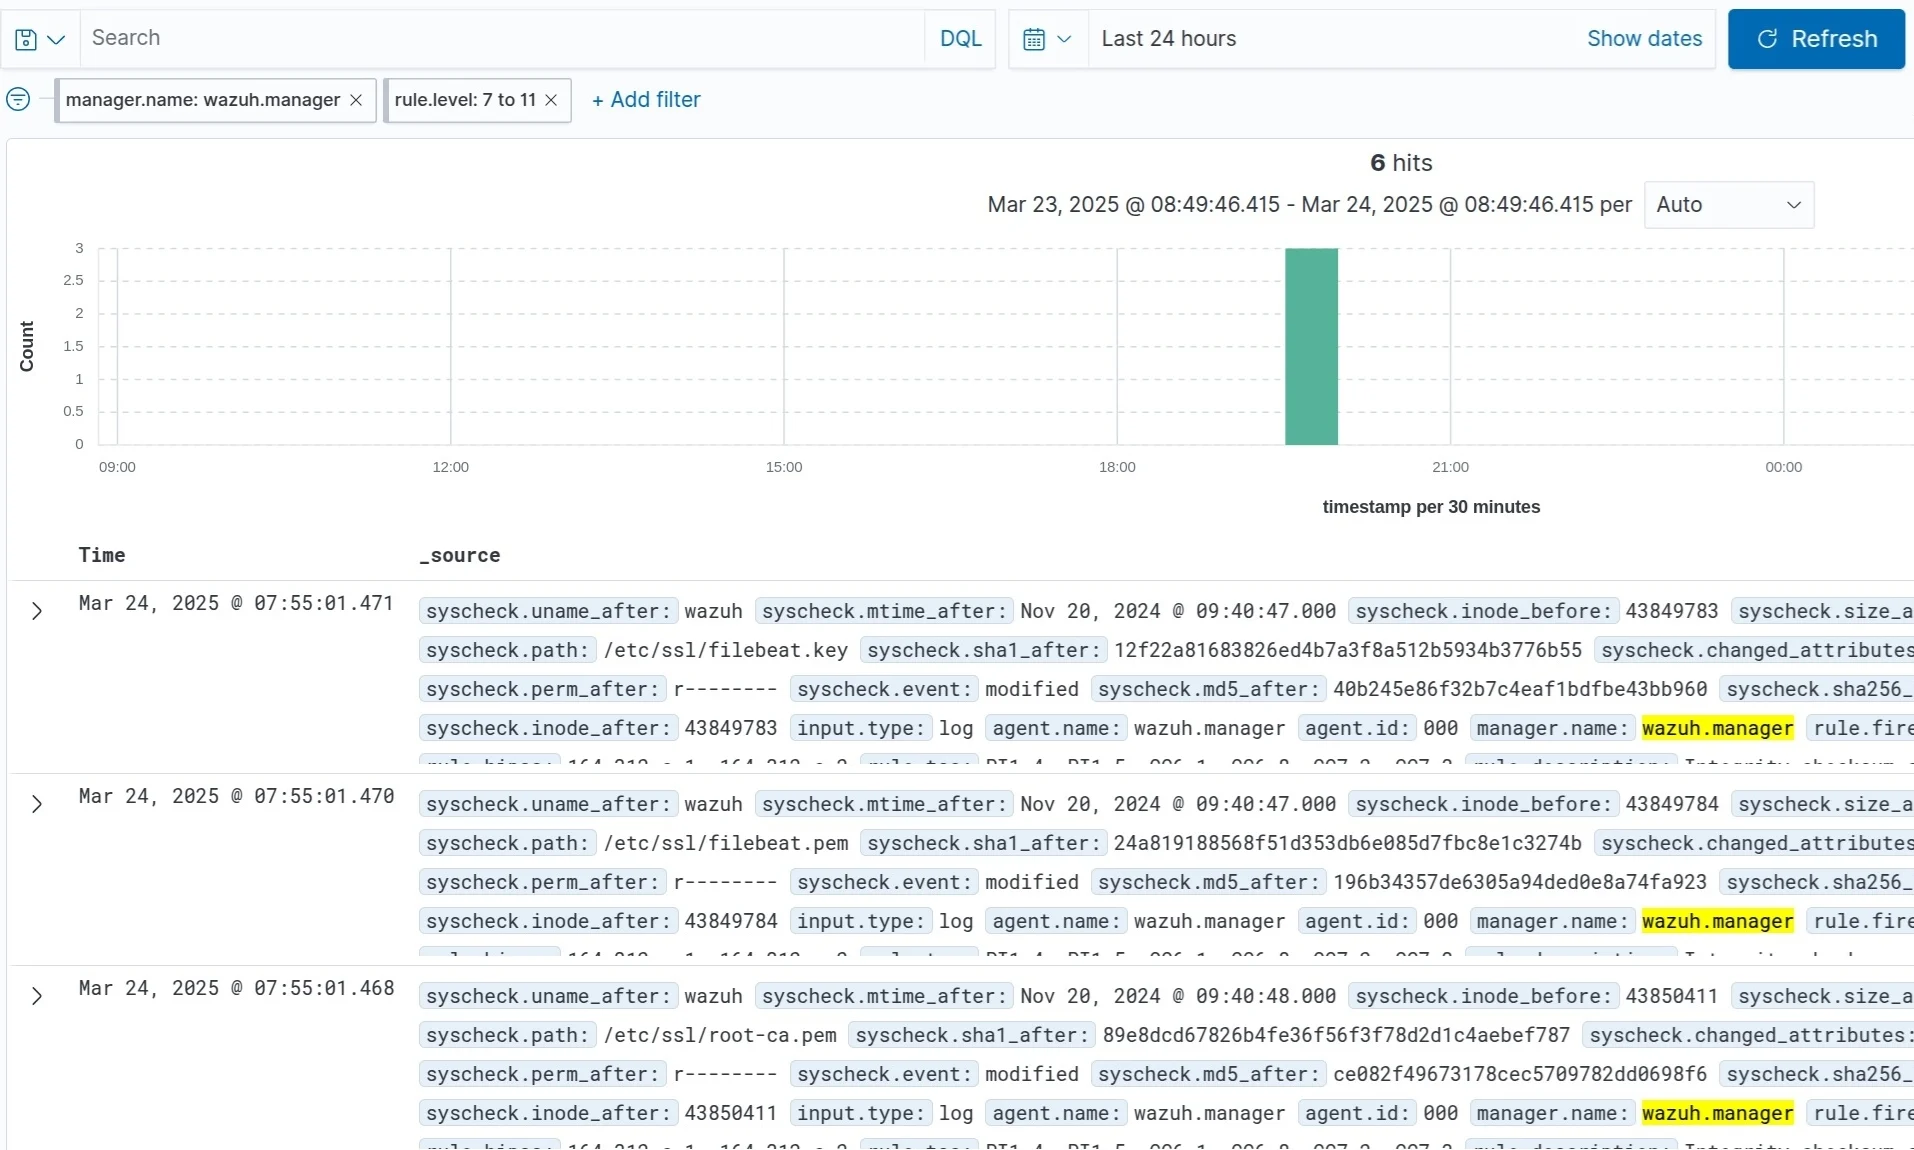
Wazuh alerts view showing file integrity events on monitored hosts

What Wazuh watches for

Unauthorized file changes

Critical files are monitored, and a change to one raises an alert with what changed, on which host and when.

Suspicious activity in the logs

System logs and processes are analyzed in real time against detection rules, so unusual behavior is flagged as it happens.

Known vulnerabilities

Hosts are scanned regularly against the CVE database, with findings ranked by severity so the riskiest fixes come first.

Weak configuration

System settings are checked against security best practices, and anything that falls short is reported.

Patterns, not just events

Events from different sources are correlated to reveal patterns that single log entries would not show on their own.

Compliance reporting

Reports map findings to applicable regulatory standards, ready for an audit rather than assembled for one.

Part of Security

Wazuh covers the endpoints within the Security capability, one of eight in the ResorsIT Platform, alongside network intrusion detection and a secrets vault.

Explore the whole platform

Under the hood

The components ResorsIT runs, connects and keeps up to date for this capability.

Wazuh Open source File integrity, log analysis, vulnerability and configuration assessment
OpenSearch Open source Where Wazuh's findings land, beside the rest of the Site's logs
Journal ResorsIT Tamper-evident record of access and changes across the platform

How Wazuh protects your hosts

Endpoint security tools are easy to buy and hard to run well. Alerts pile up in a console nobody opens, the tool needs its own logins and upgrades, and its findings never meet the rest of your operational data. ResorsIT runs Wazuh, a widely used open-source security monitoring platform, as an optional part of the Security capability, so it is installed, kept current and connected for you.

Intrusion Detection

Wazuh monitors critical files for unauthorized changes and analyzes system logs and processes to identify suspicious activity. It regularly scans systems for known vulnerabilities using the CVE database and helps prioritize remediation by severity. Events from different sources are correlated to identify patterns that individual log entries would not reveal on their own, and alerts can be routed by email, Slack or other channels based on thresholds you set.

Configuration Assessment and Compliance

Wazuh also evaluates system configurations against security best practices and generates compliance reports for applicable regulatory standards. It supports both agent-based and agentless collection, and integrates with other security tools through its REST API.

Findings Where Your Team Already Looks

On ResorsIT, Wazuh’s findings land in OpenSearch with the rest of the Site’s logs, where the Monitoring dashboards and alerts can reach them. Network-level threats are covered by Suricata, and the full picture is on the Security page. More details on Wazuh itself are at the Wazuh website.