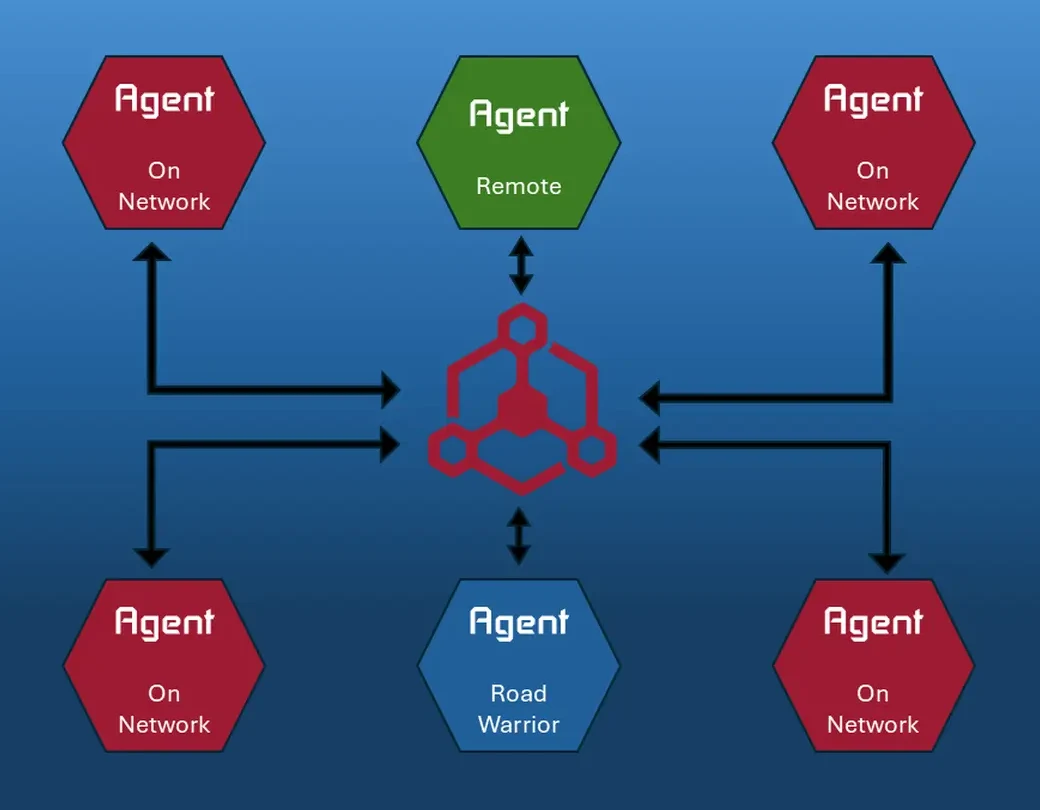
The ResorsIT agent comes from decades of experience building agent technology for IT and operational technology environments. It is deliberately small: one compiled program on each managed host, with no runtime to install alongside it, doing a short list of jobs and reporting every one of them back to the platform.
A Connection the Host Opens
The agent holds a persistent, encrypted connection to the Agent Manager, and it is the agent that opens it. A host behind NAT, a home router or a corporate firewall needs no inbound rule to stay manageable, and a laptop on the road is managed the same way as a server in the rack. If the connection drops, work is queued on the host and retried when it returns.
Commands You Can Trust
Each command is signed with Ed25519 public key cryptography, and the agent checks the signature before it runs anything. Files moving to or from the host are verified with SHA-256 hashes carried inside those signed messages. Because the platform decides which tasks the agent will accept, a compromised host cannot use the agent to run something the platform did not authorize.
Installing and Updating Software
When an installation is dispatched, the agent first checks what is already on the host, then pulls packages from the repositories or private registry that ResorsIT manages, resolves dependencies and applies configuration. The same path deploys web applications and keeps them current, and each step is logged centrally.
Auditing Hosts
The agent collects the state of the host, including installed software, running processes, open ports and user accounts, and compares it with your compliance policies. Hosts that fall out of line are reported with alerts, and common issues such as an unused open port can be fixed automatically if you choose.
Security by Design
The agent works on least privilege. File transfers use time-limited tokens issued by the Agent Manager rather than passwords kept on the host, and role-based access on the platform means administrators can dispatch only the tasks they are allowed to run. Rolling out the agent is a startup script or a configuration management run, and from then on the agent is updated centrally, without logging in to each host.